
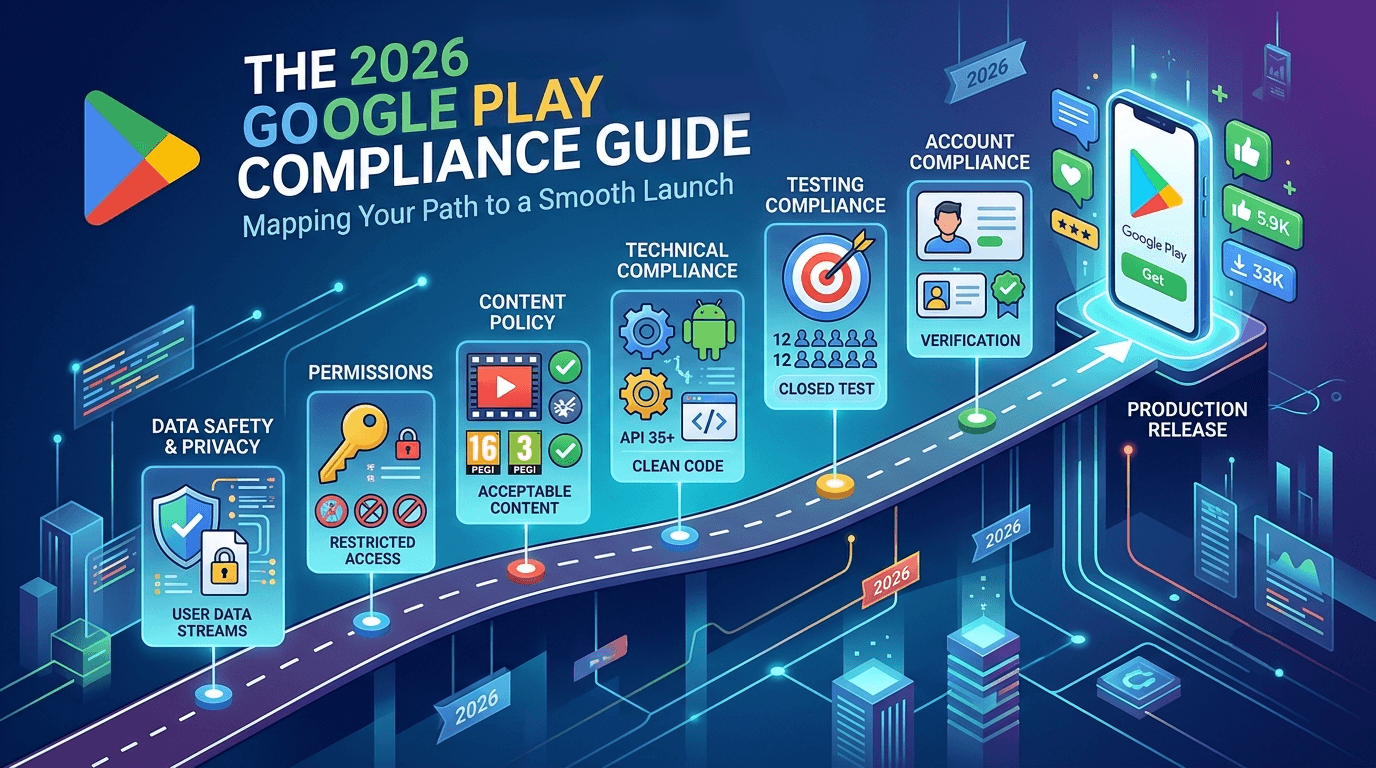
Compliance is not a single checkbox — it is a set of standards your app must meet across data, permissions, content, and testing. Falling short in any area can block your launch or trigger enforcement. This Google Play compliance guide gives developers a clear map of what compliance means in 2026 and how to achieve it.
Contents
Quick answer
Featured answer: Google Play compliance means accurate data safety declarations, a valid privacy policy, justified permissions, policy-compliant content, a current target API level, and — for new personal accounts — a completed closed test. Meeting all six keeps your app publishable and in good standing.
Data safety and privacy
- Complete the data safety form to match real behavior.
- Publish a valid privacy policy.
- Disclose third-party SDK data collection.
- Follow regional laws — GDPR, COPPA.
Permissions
Request only what your features need and justify sensitive permissions. See background location and camera and microphone.
Content policy
- Avoid restricted or prohibited content.
- Accurate content rating and target audience.
- No deceptive behavior or misleading metadata.
- Ad policy compliance — ad policy testing.
Technical compliance
- Meet the current target API level.
- Ship an AAB — AAB vs APK.
- Maintain healthy Android vitals — vitals.
Testing compliance
New personal accounts must run closed testing with 12 testers for 14 days before production. Only real, opted-in testers count — see real vs fake testers.
Tip: Meeting the testing requirement with genuine testers is a compliance step, not a shortcut. Submit your app to satisfy it with real testers.
Account compliance
- Complete identity verification — verification.
- Keep your account in good standing — avoid termination risks.
- Watch policy changes — policy changes.
Building compliance into your workflow
Compliance is far easier when it is part of how you build, not a scramble before launch. Bake these practices into your development process:
- Decide data practices up front. Know what you collect and why before you write the code, so your data safety form writes itself.
- Add permissions deliberately. Request a permission only when a feature needs it, and note the justification at that moment.
- Track your SDKs. Maintain a list of third-party libraries and what data each one touches.
- Review policy changes periodically. Google updates policies over time — see policy changes to watch.
- Re-check compliance before every release, not just the first.
Developers who treat compliance as an afterthought end up rewriting forms and stripping permissions under deadline pressure. Those who build it in barely notice it at submission time. The same discipline that keeps your first app compliant protects your account long term, reducing the risk of warnings or enforcement across everything you publish.
Data safety: your biggest compliance surface
If there is one area of compliance to get right, it is the data safety form, because inaccurate declarations here are among the most common causes of rejection. The form requires you to declare what data your app collects, how it is used, whether it is shared, and how it is protected. The catch that trips up most developers is that "your app" includes every third-party SDK you bundle — analytics, advertising, crash reporting, social logins, and more. These libraries frequently collect data in the background, and each undeclared collection becomes a mismatch between your declaration and your app's real behavior.
Getting this right requires a deliberate audit: enumerate every dependency, consult each one's documentation to learn what it collects, and make your declaration reflect the complete picture. Then treat the form as a living document, revisiting it every time you add or update a library. This discipline resolves a large share of compliance problems and demonstrates to Google that your app is exactly what it claims to be. See the detailed data safety form guide for a step-by-step approach.
Privacy policy and permissions
Two closely related compliance essentials are your privacy policy and your permissions. Most apps require a valid, publicly accessible privacy policy URL that accurately describes your data practices, and it must be consistent with your data safety declarations. A missing, broken, or inconsistent privacy policy is a frequent and easily avoided rejection cause. Publish a clear policy, link it correctly, and keep it aligned with what your app actually does. See privacy policy requirements.
Permissions demand a minimalist philosophy: request only what a visible feature genuinely needs, and be able to justify each one. Sensitive permissions — location, camera, microphone, contacts, SMS — draw heavy scrutiny, and requesting them without a clear purpose is a common violation. Background location is especially sensitive with its own strict requirements. Audit your permissions the same way you audit your SDKs, removing anything speculative or unused. Minimal, justified permissions not only avoid rejections but also build user trust. See background location and Play Store review.
Content policy and target audience
Content compliance governs what your app contains and does. Restricted categories, user-generated content without moderation, intellectual property you lack rights to, and deceptive behavior can all trigger enforcement. Importantly, content policy applies during testing as well as at production, so your build should comply from the very first upload rather than being cleaned up later. Review the relevant policies for your app's category and ensure your content aligns before you submit anything.
Target audience settings add another layer, especially if your app might appeal to children. Apps directed at kids face additional families-policy requirements around content, ads, and data collection, and misclassifying your audience can lead to serious compliance problems. Set your target audience honestly and understand the obligations that come with it. Getting audience and content right early prevents category-specific rejections that can be difficult to untangle after the fact.
Developer verification and account standing
Compliance is not only about your app — it is also about your account. Google requires developer identity verification, and an incomplete verification can block publishing regardless of how compliant your app is. Complete it early so it never becomes a finish-line obstacle. Beyond verification, your account's standing matters: prior policy strikes or warnings can affect future submissions, and repeated violations can escalate to serious enforcement, including termination.
Protecting your account standing is a long-term compliance priority, because your account is the home for every app you will ever publish. Avoid shortcuts that carry enforcement risk — most notably, never use fake installs or bots to satisfy the testing requirement, since abuse signals can attach to your account and outlast any single app. See account termination risks and developer identity verification for the specifics.
Staying compliant over time
Compliance is not a one-time event but an ongoing responsibility, because Google's policies evolve and your app changes. New policy requirements are announced periodically, target API level requirements rise annually, and each dependency you add can introduce new data practices to declare. The developers who avoid trouble are those who treat compliance as a habit: they keep their data safety form current, watch for policy announcements, meet updated technical requirements on schedule, and re-audit when they add features or libraries.
Building this habit early makes every future release smoother. Rather than facing a compliance scramble with each update, you maintain a continuously accurate picture of what your app does and how it complies. This proactive stance is far less stressful than reactive firefighting after a rejection, and it steadily builds the kind of clean account history that makes Google's systems treat you as a trusted developer. See target API level requirements.
Compliance and testing go hand in hand
A point worth emphasizing is that compliance and the closed testing requirement are connected, not separate hurdles. Policy checks apply during testing, not only at production, which means your testing build must already be compliant. If your data safety form is inaccurate or your permissions are unjustified while you are in closed testing, those issues can surface and block your path to production even after a completed 14-day window. Treating testing as a compliance-free zone is a costly mistake.
The productive way to view this is that your testing window is also a compliance validation period. Use those two weeks to confirm your declarations match your app's real behavior, that your permissions are all justified, and that your content follows policy. Fixing a compliance issue discovered during testing is far less painful than discovering it at the production gate. By the time your window closes, your app should be both tested and demonstrably compliant, so your production application faces no surprises. This dual-purpose view of the testing window — quality and compliance together — is what separates smooth launches from frustrating ones.
A practical compliance checklist
To make compliance concrete, work through a simple checklist before you apply for production. Confirm your data safety form declares everything your app and its SDKs collect and share. Verify your privacy policy is live, linked, and consistent with your declarations. Ensure every permission maps to a visible feature and that sensitive permissions are justified. Check that your content complies with policy and your target audience is set honestly. Confirm your app meets the current target API level. Complete identity verification. And make sure no outstanding tasks or warnings remain on your Play Console dashboard.
Running this checklist converts the abstract idea of "being compliant" into a series of concrete, verifiable actions. Each item you clear removes a potential rejection cause, and an empty dashboard task list is a strong signal that you are ready to submit. Because compliance is ongoing rather than one-time, revisit this checklist whenever you add a dependency or ship a significant update. Making it a routine part of every release keeps you continuously compliant and turns what feels like a daunting requirement into a manageable habit. See target API level requirements.
Compliance when you ship updates
Compliance is not finished at launch — it must be maintained with every update, and this is where some developers slip up after an initially clean release. Each time you add a feature or a new third-party library, you may introduce new data practices that must be reflected in your data safety form, or new permissions that must be justified. An update that quietly adds an analytics SDK without updating your declarations can turn a compliant app into a non-compliant one. Treating your data safety form as a living document you revisit with each release keeps you continuously accurate.
Policy requirements also evolve over time. Google raises target API level requirements annually and periodically introduces new policies, so an app that was compliant last year may need changes to stay compliant this year. Staying aware of policy announcements and meeting updated technical requirements on schedule prevents your app from falling out of compliance through no fault of a specific change. The developers who avoid nasty surprises are those who treat compliance as an ongoing responsibility woven into their release process, rather than a one-time hurdle cleared at launch. Building this habit early makes every future update smoother and keeps your account in consistently good standing. See target API level requirements.
Key takeaways
- The data safety form is your biggest risk — declare exactly what your app and SDKs do.
- Keep a valid privacy policy consistent with your declarations.
- Request minimal, justified permissions, especially sensitive ones.
- Comply with content and audience policies from the first upload.
- Verify early and protect account standing — compliance is ongoing, not one-time.
Frequently asked questions
What is the biggest compliance risk?
Inaccurate data safety declarations and unjustified permissions.
Does compliance apply during testing?
Yes. Policy checks apply during closed testing, not only at production.
How often do policies change?
Regularly. Review the Policy section and Google's announcements periodically.
Is a privacy policy always required?
In nearly all cases, yes — especially if you collect any data.
Can non-compliance terminate my account?
Serious or repeated violations can, so treat compliance seriously.
Do I need to re-check compliance for updates?
Yes. Every release should be re-checked, because new features, SDKs, or permissions can change your data practices and require updated declarations before you ship the update.
Does closed testing count as compliance?
Yes, it is a required step for new personal accounts.
Key takeaways
- Compliance covers data safety, privacy, permissions, content, technical standards, and testing.
- Your data safety form must match your app's real behavior, including third-party SDKs.
- Request only the permissions your features need, and justify sensitive ones.
- Meet the current target API level and maintain healthy Android vitals.
- Build compliance into your workflow so it is routine, not a last-minute scramble.
Conclusion
Compliance spans data, permissions, content, technical standards, testing, and account health. Address each area deliberately and your app stays publishable and safe from enforcement. Need to satisfy the testing requirement with real testers? Submit your app today.
Expanded for topical authority — additional practical sections below. Original guide content above is unchanged.
Real-world scenarios: who this matters for
The guidance in this article on Google Play Compliance Guide for Developers applies across many Android product types. Use these scenarios to map the advice to your situation.
| Developer type | Typical challenge | Practical focus |
|---|---|---|
| Indie / solo | Limited tester network and time | Start closed testing early; keep a buffer above 12 opted-in testers; parallelize listing + Data safety work |
| Startup | Launch deadline vs 14-day rule | Treat the window as fixed; recruit in parallel with QA; avoid last-minute track setup |
| Agency / white-label | Multiple client apps, each needing its own test | One closed test per app; standardize opt-in onboarding; track eligibility dates per client |
| Flutter / React Native | Cross-platform build + Play Console quirks | Ship a signed AAB to closed testing; verify installs from Play, not sideload; watch vitals on mid-range devices |
| Native Kotlin | Device/API fragmentation | Cover API levels and OEMs in your tester mix; fix crashes before requesting production |
| Game / Unity | Performance + retention during 14 days | Keep testers engaged so count never dips below 12; monitor ANRs and battery |
| E-commerce / fintech | Policy + payment flows | Test checkout, permissions, and declarations carefully before production access |
| Healthcare / kids / education | Sensitive policies (Families, data) | Align listing, privacy, and content rating with real app behavior during the test window |
Visual placeholder: Scenario matrix infographic — Indie / Startup / Agency / Cross-platform paths for Google Play Compliance Guide for Developers.
Closed testing vs other Play tracks (quick reference)
Context for Google Play Compliance Guide for Developers: choose the right track so you do not waste the 14-day window on the wrong workflow.
| Track | Purpose | Counts toward 12×14? | Typical use |
|---|---|---|---|
| Internal testing | Fast private builds | No | Shake out bugs before the counted window |
| Closed testing | Private / invite testers | Yes (for new personal accounts) | Meet production-access requirement + QA |
| Open testing | Public beta | Not a substitute for the closed requirement | Broader feedback after closed eligibility |
| Production | Public release | N/A | After access approved + review |
Visual placeholder: Timeline — Internal → Closed (14 days) → Production request → Staged rollout.
Common mistakes (and how to avoid them)
These mistakes repeatedly show up when developers work through Google Play Compliance Guide for Developers:
- Confusing invited vs opted-in testers — Only testers who open the opt-in link and install from Play count toward 12. Check the opted-in number in Play Console, not your email list.
- Recruiting exactly 12 with no buffer — One uninstall can break continuity. Aim for ~15 active opted-in testers.
- Starting the counted clock late — Listing assets, Data safety, and privacy work should run during the 14 days, not after.
- Using sideloaded APKs or fake installs — They do not satisfy Play’s closed testing expectations and can create account risk.
- Ignoring tester feedback until day 14 — Crashes that drive uninstalls threaten your streak and your review outcome.
- Requesting production access before the continuous streak completes — Eligibility checks fail even if calendar time has passed.
Troubleshooting checklist
If something feels “stuck” while applying Google Play Compliance Guide for Developers, walk this list before changing strategy:
| Symptom | Likely cause | Fix |
|---|---|---|
| Console shows < 12 testers | Invites sent but not opted in | Resend opt-in link; confirm install from Play |
| “Not eligible” after 14 calendar days | Count dipped below 12 mid-window | Restore 12+ and complete a full continuous streak |
| Tester cannot join | Wrong account, Group lag, or track not published | Verify Google account, Group membership, track release |
| App fails to install | Device/API mismatch or signing issue | Check AAB, minSDK, Play App Signing |
| Production still rejected after testing | Policy, declarations, or stability — not the clock | Read the exact reason; fix that category completely |
Visual placeholder: Troubleshooting flowchart for Google Play Compliance Guide for Developers.
Action checklist
Use this checklist alongside the rest of this guide on Google Play Compliance Guide for Developers:
- ☐ Closed testing track created with a signed release (AAB)
- ☐ Opt-in link tested on a fresh Google account
- ☐ At least 12 testers opted in (prefer ~15)
- ☐ Daily check that opted-in count stays ≥ 12 for 14 continuous days
- ☐ Core flows exercised (login, main feature, permissions, offline/online)
- ☐ Crashes / ANRs triaged from tester reports and vitals
- ☐ Store listing, screenshots, and feature graphic drafted
- ☐ Privacy policy + Data safety + content rating aligned with real behavior
- ☐ Production access requested only after eligibility is green
- ☐ Staged rollout plan ready for first public release
Additional FAQs developers ask about Google Play Compliance Guide for Developers
Quick answer: what should I do first?
Confirm you are on a closed testing track with real opted-in installs, keep 12+ testers for 14 continuous days, and fix policy/stability issues in parallel. Then use the detailed sections above for Google Play Compliance Guide for Developers.
Does this apply to organization (company) accounts?
The classic 12×14 closed testing gate is primarily associated with new personal developer accounts. Always verify your account type and current Play Console eligibility messaging for your app.
Do friends and family count as testers?
Yes — if they opt in via your closed testing link and install from Google Play. They only help if they stay opted in for the continuous period.
Can I update the app during the 14 days?
You can usually push updates on the closed track, but unstable releases that cause uninstalls can threaten your tester count. Prefer polishing via internal testing first when possible.
What if production access is still rejected?
Read the exact reason. Incomplete testing is only one category — policy, Data safety mismatches, and crashes are common. Fix the cited issue fully before reapplying.
Is paying for testers allowed?
Using real people who install from Play is what matters. Avoid fake install farms. A one-time managed service that supplies real closed testers is a practical option when DIY recruitment is too slow.
How is Fast Testers different from free communities?
Free communities trade time and mutual availability. Fast Testers assigns about 15 real testers after you submit a valid closed testing link (one-time $15 per app) and includes a production access guarantee under its refund terms.
Where should I go next?
Review the related guides below, then either finish DIY recruitment or start closed testing if you need speed and continuity.
Sources, updates, and how to use this guide
This article on Google Play Compliance Guide for Developers is maintained for Android developers preparing Google Play closed testing and production access. Always cross-check eligibility text inside your own Play Console, because Google’s UI labels and account rules can vary by account type and date.
- Primary official references: Google Play closed testing help, Developer Program Policies, and Play Console eligibility messaging for your app.
- Practical experience lens: guidance here reflects common failure modes indie developers and agencies hit when recruiting testers, maintaining the 14-day streak, and recovering from production-access rejections.
- Last reviewed focus: 12×14 closed testing continuity, real vs fake testers, and parallel listing/compliance work during the window.
Related guides and next steps
Continue building topical depth around Google Play Compliance Guide for Developers with these Fast Testers resources:
- Agency Guide Testing Client Apps On Google Play
- Education Apps And Google Play Compliance Testing
- Finance Apps Google Play Testing And Compliance
- Gdpr Compliance For Android Apps On Google Play
- Google Play Closed Testing Guide How To Get 12 Testers For 14 Days
- Google Play Console Beginner Guide
- Google Play Developer Account Guide
- Google Play Store Submission Guide
- Pricing — $15 closed testing
- How Fast Testers works
- FAQ
- Developer reviews
- Case studies
- Submit your app / start closed testing
Need reliable testers so your 14-day streak does not stall? Educate first with the guides above, then start when you are ready — one-time pricing, real Play installs, dashboard tracking.
Further expansion — case study, decisions, and expert recommendations. Prior sections remain unchanged.
Case study: first Play launch planned around the closed testing window
Problem: A small SaaS team treated Google Play publishing like iOS TestFlight — they expected to upload and go public the same week. They discovered the personal-account closed testing gate mid-sprint.
Solution: They reframed the sprint around Google Play Compliance Guide For Developers: internal testing for crash triage first, then closed testing with a buffer of testers, while design finished screenshots and legal finished privacy/Data safety in parallel.
Result: The 14-day requirement stopped feeling like “dead time.” When eligibility flipped green, listing and declarations were already ready, so production review was the only remaining gate.
Lessons learned:
- Start the closed track as soon as the build is stable enough to keep installed.
- Parallelize compliance work inside the window.
- Protect the streak like a production SLA.
Decision guide: what should you do next?
Use this decision path when applying Google Play Compliance Guide For Developers:
- Is your account a new personal developer account that still needs production access?
If yes, plan for closed testing with 12+ opted-in testers for 14 continuous days. If no, still test — but confirm the exact eligibility text in Play Console. - Do you already have 12+ reliable people who will install from Play and stay for two weeks?
If yes, DIY can work — add a buffer and monitor daily. If no, use community exchange or a managed closed testing service. - Is your build stable enough that testers will not churn?
If no, run internal testing first. Entering the counted window with crash loops is how streaks die. - Are Data safety, privacy policy, permissions, and listing aligned with real behavior?
If no, fix during the window so production review does not bounce you after the clock. - Has production access been rejected?
Classify: eligibility vs policy vs declarations vs stability. Fix that category completely, then re-test / re-request.
Visual placeholder: Decision tree diagram for Google Play Compliance Guide For Developers (DIY vs managed vs fix-and-retry).
Expert recommendations
- Instrument the streak: Check opted-in count daily for the first week; replace dropouts same day.
- Brief testers once: Send a short checklist (install from Play, open app daily, try core flow, report crashes). Silent testers still count if opted in — engaged testers protect quality.
- Never “solve” recruitment with fake installs: It fails the intent of closed testing and can create account risk.
- Ship a boring-stable build to closed testing: Save experimental features for internal tracks.
- Educate first, then accelerate: If your blocker is simply finding real testers fast, a one-time managed option (Fast Testers: 15 testers, $15/app) is often cheaper than slipping a launch.
For hands-on setup after reading about Google Play Compliance Guide For Developers, see how it works and pricing, or submit your closed testing link when you are ready.
Internal navigation hub — added to strengthen topical connections. Original article content above is unchanged.
Continue learning
- GDPR Compliance for Android Apps on Google Play — Learn about GDPR requirements for Google Play closed testing. Complete guide for Android developers publishing.
- Google Play Closed Testing Guide: How to Get 12 Testers for 14 Days — Stuck on the Google Play Console closed testing track? Learn how to successfully recruit 12 active testers, ma.
- Google Play Developer Account Guide — A complete Google Play developer account guide: registration, identity verification, personal vs organization .
- COPPA and Kids Apps on Google Play Store — Learn about COPPA compliance for Google Play closed testing. Complete guide for Android developers publishing .
- Google Play – 12 Testers for 14 Days — Everything you need to know about Google Play's closed testing requirement..
- Google Play Data Safety Form and Closed Testing — Learn about data safety requirements for Google Play closed testing. Complete guide for Android developers pub.
Next steps
- Ready to run closed testing with real Android testers? Submit your app or see pricing ($15 one-time).
- Compare options on our testing service comparison page, or read developer reviews and case studies.
- Still deciding? Review how Fast Testers works and the FAQ.